




Read More

Night Recap - November 2, 2026
4 hours ago
HK braces for cooler weather after warmest Oct on record
01-11-2026 17:53 HKT
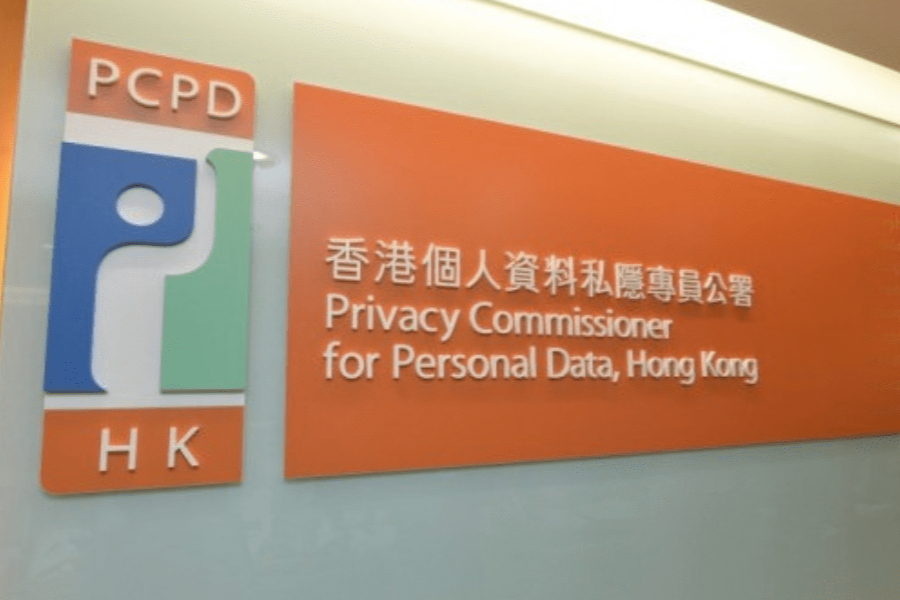
The Office of the Privacy Commissioner for Personal Data (PCPD) has launched formal investigations into recent data breach notifications from several high-profile companies in Hong Kong.
The affected businesses include airlines Cathay Pacific, Hong Kong Airlines, and Malaysia Airlines Berhad, alongside major electrical appliance retailers YOHO Hong Kong and Broadway.
Amid a rising global threat of cyberattacks, the privacy regulator disclosed that as of late October 2026, it had already received dozens of complaints and enquiries, with individual victim financial losses ranging from HK10,000 to more than HK1.5 million.
In the wake of these security incidents, the privacy commissioner is urging citizens to maintain extreme vigilance against sophisticated scams.
Fraudsters frequently exploit leaked purchase histories and flight details to craft convincing phishing messages or impersonate company representatives, often claiming they can arrange product returns, compensation, or flight refunds.
The watchdog cautioned that real merchants will never ask customers for upfront deposits, handling fees, or bank transfers simply to verify an account.
To protect their personal privacy and financial assets, members of the public should avoid opening suspicious links or attachments, verify caller identities through official company channels or physical stores, keep records of fraudulent communications, and monitor their online accounts for unauthorized activity.
Suspected data misuse can be reported directly to the PCPD's dedicated fraud prevention line, while potential criminal fraud should be reported to the police immediately.
Beyond public warnings, the regulator reminded commercial organizations of their legal obligations to safeguard customer information under Hong Kong's privacy laws. Under Data Protection Principle 4 of the Personal Data (Privacy) Ordinance, companies must take all practical steps to prevent unauthorized access, loss, or misuse of personal data.
Pointing out that prevention is far better than remediation, the commissioner stressed that organizations relying on external vendors must enforce strict third-party risk management.
Recommended safeguards include thoroughly vetting service providers, limiting data transfers to what is strictly necessary, clearly defining access rights based on job roles, requiring instant breach notifications, and routinely auditing vendor systems for unusual login behavior or large data transfers.