

Read More
The police on Monday noted that a security gap in the online checkout process—which bypassed the standard requirement for one-time verification passwords—has enabled scammers to ring up HK$25 million in fraudulent charges during the launch of Apple's latest smartphone series.
ADVERTISEMENT
SCROLL TO CONTINUE WITH CONTENT
During the initial two days of pre-orders over the weekend, police had already logged complaints from more than 700 individuals involving roughly HK$14.7 miilion, with the single largest case reaching approximately HK$114,000.
Police confirmed that as of Monday afternoon, 1,209 residents had filed formal reports after discovering their compromised cards had been used without authorization to purchase new devices on the official online store.
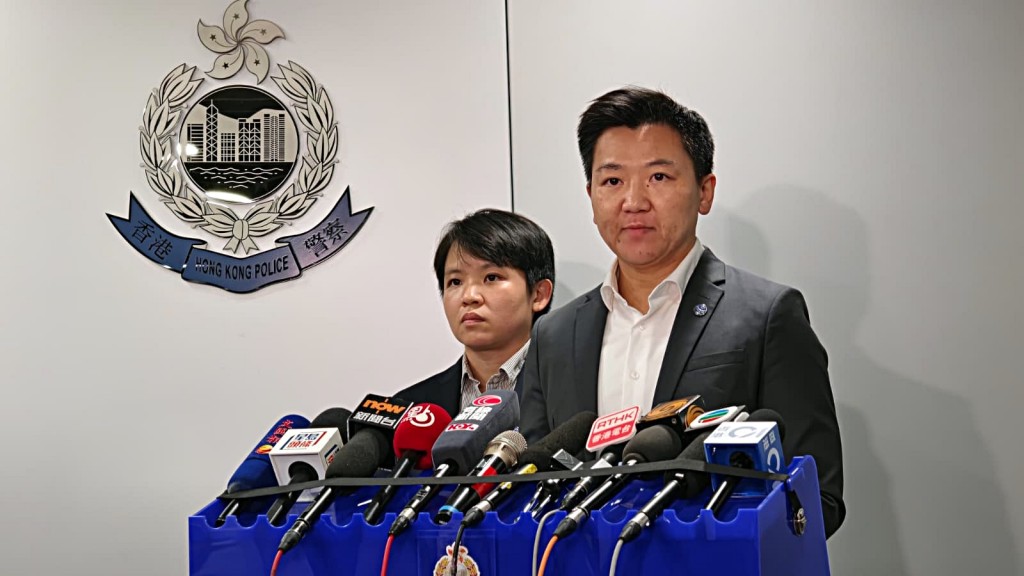
The case has been formally classified as obtaining property by deception. During a media briefing on Monday evening, Superintendent Cheung Hou-yee of the Technology Crime Division stated that complaints began flooding online forums and social media platforms shortly after pre-orders opened on Saturday evening.
Unsuspecting cardholders were blindsided by sudden automated bank notifications confirming steep charges for flagship handsets that they had never ordered, with individual losses reaching as high as HK$114,000.
Absence of one-time passwords exposed systems to abuse
Addressing public concerns over whether the merchant platform had suffered a security breach, Chief Inspector Chan Lai-yu explained that preliminary technical inspections conducted by both Apple and the affected banks confirmed all network systems were operating normally with no signs of external hacking.
However, investigators identified a significant procedural gap in the online checkout system, which did not require customers to enter a one-time password via SMS or undergo two-factor authentication.
This absence of real-time identity verification allowed fraudsters holding leaked credit card credentials to execute high-value transactions automatically without alerting the cardholders beforehand.
Multi-pronged investigation launched alongside emergency transaction freeze
To prevent further financial damage, the cyber crime unit has established an emergency liaison mechanism with Apple and issuing banks to cross-reference police report data, allowing institutions to intercept suspicious transactions and cancel fraudulent orders swiftly.
Authorities are pursuing the syndicate across two primary investigative fronts.
Detectives are analyzing whether victims share common points of compromise, such as prior phishing scams or data leaks on shared platforms, while simultaneously tracing the digital footprints of those placing the orders to identify the individuals and criminal syndicates orchestrating the scheme.
Investigators have formally obtained detailed transaction logs and are coordinating closely with the Hong Kong Monetary Authority.
Cardholders urged to take immediate four-step protective action
Police issued an urgent advisory outlining a four-step response for anyone suspecting their payment credentials have been misused.
Victims should first immediately freeze or lock their cards through mobile banking apps or bank hotlines, and then contact Apple customer service to request the cancellation of the fraudulent orders.
Affected individuals should subsequently file a report via the online reporting portal or at a local police station to obtain an official case reference number, which must then be submitted to their issuing bank to facilitate the formal chargeback and dispute process.
Authorities reminded the public to maintain strict vigilance over sensitive financial information and avoid entering card credentials on unfamiliar websites.