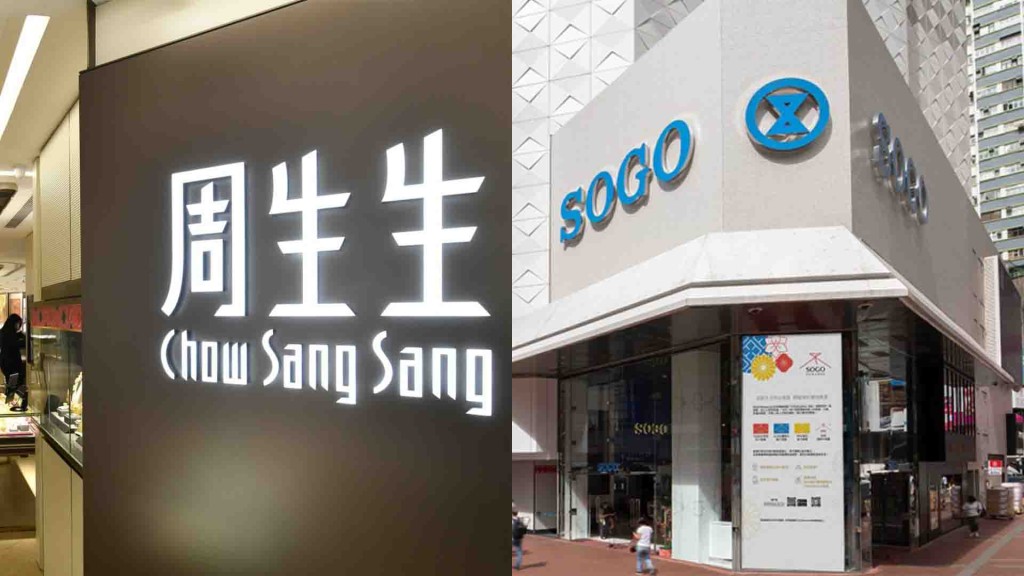
SOGO and Chow Sang Sang have both reported unauthorized access to their systems, with the Privacy Commissioner for Personal Data saying the SOGO incident may affect about 820,000 members.
SOGO says member data accessed without authorization
SOGO said it discovered in November that unauthorized parties had accessed some data in its membership system. Based on preliminary investigations, the affected data mainly involved some members' membership numbers, names, contact phone numbers, email addresses and membership points.
The company said it takes the incident seriously, has launched a full investigation, notified relevant government departments and is fully cooperating with authorities.
It said it has strengthened cybersecurity monitoring, abnormal activity detection and risk assessments, and is continuously monitoring system operations to prevent similar incidents.
SOGO urged members to stay alert, not to click on unknown links and not to disclose personal, account or verification information to third parties in response to suspicious calls, messages or emails claiming to be from the company.
The Privacy Commissioner's Office said it received a data breach notification from SOGO on Thursday. Preliminary information showed SOGO discovered abnormal data reading records in its membership system on November 5, and the incident may affect about 820,000 members' personal data, possibly including names, email addresses, phone numbers and membership points balances. It has launched an investigation.
Chow Sang Sang says system accessed without authorization
Chow Sang Sang Group said it recently discovered unauthorized access to parts of its system, possibly involving member and employee data, first identified on Wednesday. The group said it immediately took measures to stop malicious access and strengthen system security, and engaged cybersecurity experts to investigate and advise.
The group's website was showing a "under maintenance" notice and could not be accessed.
Chow Sang Sang said it has notified the Privacy Commissioner's Office and police, and is notifying potentially affected customers. It said it will continue monitoring the situation and cooperating with investigations.
Preliminary findings indicate affected customer data may include member names, contact phone numbers, email addresses, some order details and the last four digits of credit card numbers. Affected employee data may include names, positions, company email addresses and contact numbers.
The group urged customers to be wary of calls, messages or emails impersonating the group, financial institutions or e-payment platforms, and not to click on unknown links or disclose credit card details, verification codes, account passwords or other sensitive personal data.
It apologized for any inconvenience and concern caused, and said it will continue monitoring the situation and provide updates on any major developments.